
Science & Technology
Moderna COVID-19 shot more likely to cause heart inflammation than Pfizer’s, study shows

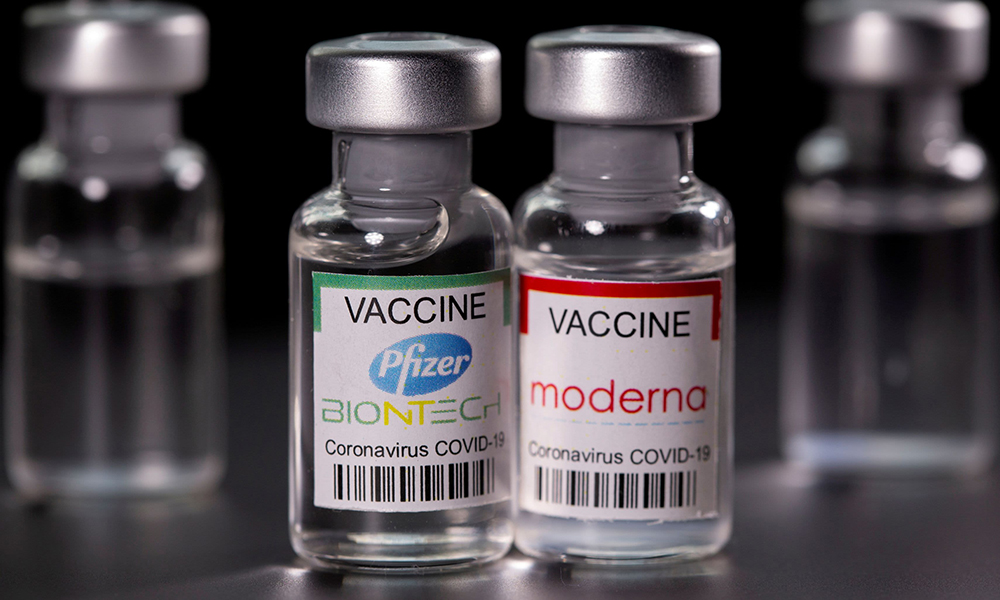
Moderna’s COVID-19 vaccine is up to four times more likely to cause inflammation of the heart muscle, a very rare side effect, than its rival vaccine from Pfizer-BioNTech, according to a Danish study published in the British Medical Journal late on Thursday.
The study, in which almost 85% of Danes, or 4.9 million individuals, aged 12 and older participated, investigated the link between mRNA-based COVID-19 vaccines and heart inflammation, also known as myocarditis or myopericarditis.
Earlier studies from Israel and the United States have indicated an increased risk of heart inflammation after inoculation with the mRNA-vaccines developed by Pfizer-BioNTech and Moderna.
“Vaccination with mRNA-1273 (Moderna’s vaccine) was associated with a significantly increased risk of myocarditis or myopericarditis in the Danish population,” the study said.
However, the overall risk of getting heart inflammation from the vaccines, both of which are based on mRNA-technology, was low, according to the study, conducted by researchers from Denmark’s Statens Serum Institute.
“In general, the rate of myocarditis or myopericarditis was about threefold to fourfold higher for mRNA-1273 (Moderna) vaccination than that for BNT162b2 (Pfizer-BioNTech) vaccination,” the study said.
The researchers found only 1 case per 71,400 vaccinated with Pfizer-BioNTech and 1 case per 23,800 vaccinated with Moderna. Most of the cases had been mild, the study said.
Pfizer-BioNTech’s vaccine was only associated with a higher risk of heart inflammation among women, the study said, contrasting with the results of the studies from Israel and the United States.
The authors said the discrepancy could be explained by the average age of the vaccinated population, the time span between the first and second shot, or because fewer Danes had tested positive for COVID-19.
“Our findings do not generally overshadow the many benefits that come with being vaccinated,” study author Anders Hviid said in a statement.
“One must keep in mind that the alternative of getting an infection with COVID-19 probably also involves a risk of inflammation in the heart muscle,” Hviid said.

Science & Technology
Governments take websites offline as critical cyber flaws trigger global alert
Security patches were released prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
Governments and organisations across Europe and beyond have taken websites and online services offline after the discovery of two critical vulnerabilities in widely used web software triggered an international cyber-security alert.
The vulnerabilities affect PHP, a programming language used extensively to operate websites and online applications. Attackers could potentially exploit the flaws to execute malicious code remotely on vulnerable servers, threatening sensitive information and digital infrastructure.
Security patches were released on Wednesday, October 21, prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
The Netherlands, Finland, France, Belgium and Germany have also reported precautionary shutdowns affecting government websites and other public-facing services.
In the Netherlands, affected platforms included Overheid.nl, MijnOverheid.nl and DigiD. The country’s National Cyber Security Centre also temporarily took its own website offline.
Finland’s state IT services provider, Valtori, suspended public government web services as a precaution, while France’s Interior Ministry temporarily took the websites of local administrative authorities offline.
In Belgium, the Foreign Ministry took its websites offline amid concerns about potential exploitation, although the country’s cybersecurity centre said it had not observed attacks on Belgian websites at the time.
Germany’s federal IT service provider also temporarily disabled several websites, with officials saying the measure was precautionary and no security incidents were known to have occurred.
The disruption extended beyond government agencies. Websites and online services belonging to hospitals, educational platforms and other organisations were also affected, highlighting the potential reach of vulnerabilities in widely deployed software.
In Australia, the Australian Cyber Security Centre’s website, cyber.gov.au, was among the government services affected by the security alert. Australian authorities said they were not aware of active exploitation of the vulnerabilities.
In the United States, the National Security Agency and other cybersecurity authorities urged organisations to prepare for immediate updates and take vulnerable systems offline if they could not be secured promptly. The Wikimedia Foundation, which operates Wikipedia, also took some systems offline as a precaution while addressing the flaws.
Cybersecurity company Cloudflare reported seeing early attacks associated with the vulnerabilities, although reports of exploitation do not establish that every affected organisation suffered a breach.
The incident highlights the risks created by the internet’s reliance on shared software. PHP is used across a substantial proportion of websites, meaning a single vulnerability can affect organisations in multiple countries and sectors simultaneously.
Security specialists have urged website operators to identify affected systems, install the relevant patches and examine server logs for signs of unauthorised access. Applying an update may prevent further exploitation, but organisations must also investigate whether attackers gained access before their systems were secured.
Authorities have not established that all affected websites were breached. The precautionary shutdowns are intended to reduce exposure while administrators apply fixes and verify that their systems are safe to restore.
The alert has underscored the challenge facing governments and businesses in responding to critical software vulnerabilities that can rapidly become an international security concern.
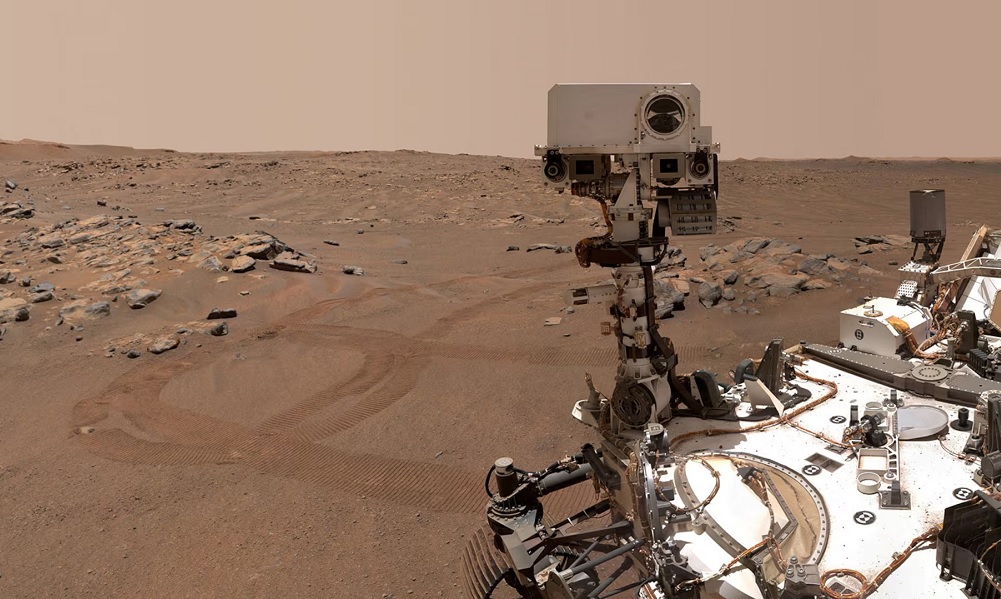
NASA’s robotic Perseverance rover has now driven farther than any other vehicle on the surface of any world other than Earth, racking up 28.1 miles (45.2 km) since arriving on Mars in 2021, the US space agency said on Tuesday.
The car-sized, six-wheeled rover reached the milestone 5-1/2 years into its mission to explore if conditions conducive to microbial life ever existed on Earth’s neighbor, Reuters reported.
In doing so, it is visiting some of the most ancient terrain ever encountered in the solar system.
“Perseverance’s engineering hardware and instruments are in excellent shape with all redundant systems still available,” Steven Lee of NASA’s Jet Propulsion Laboratory in California, told Reuters.
“A recent assessment of all systems concluded that they are capable of operating well into the 2030s, likely beyond,” added Lee, the project manager for NASA’s two Mars rovers, Perseverance and Curiosity.
Perseverance has exceeded the previous figure of 28.06 miles (45 km) driven on the Martian surface by NASA’s Opportunity rover from 2004 to 2018. Both also exceeded the driving distances of any lunar rover.
TRAVERSING JEZERO CRATER
Perseverance, with its suite of scientific instruments, has focused on the Jezero Crater, a region in the northern hemisphere of Mars believed to have been flooded with water and home to a lake basin billions of years ago.
The rover set the milestone in a journey toward an area called Idubi, through the region off the crater’s western rim nicknamed Lac de Charmes.
Its companion rover, Curiosity, rolls along in the Gale Crater near the Martian equator.
Perseverance is showing no signs of slowing down, Lee added.
Its mobility system mechanisms are being tested to show it can drive 100 km (62 miles) or more, he said, with the hardware to be tested to the equivalent of 150 km to 300 km (93 miles to 186 miles) in the effort.
NASA attributed a major role in Perseverance’s success to its self-driving capability, an autonomous navigation system called AutoNav. Lee said 90% of its drives are done autonomously, with no human intervention.
“Perseverance takes stereo images of the terrain ahead, generates a 3D software map, and selects the safest path towards a drive goal,” he said.
Another key component is the Vision Compute Element, a fast co-processor computer that allows the rover to process images and run its self-driving software very quickly, almost continuously during drives, Lee added.
That contrasts with previous rovers, which needed to pause to “think” before each drive segment, he said.
“Perseverance builds on the 29-year legacy of our past Mars rovers — Sojourner, Spirit, Opportunity and Curiosity — each incorporating prior lessons and improving our ability to drive on another world,” Lee said.
POTENTIAL BIOSIGNATURE
Lee said the rover’s biggest achievement was almost certainly its discovery, unveiled last year, of a potential biosignature, or possible sign of ancient microbial life.
This was found in reddish rock believed to have formed 3.2 billion to 3.8 billion years ago in a river channel feeding the lake that once filled Jezero Crater.
The Lac de Charmes terrain, Lee said, may yield clues to early planetary geological processes, such as the effects of large meteorite impacts. Jezero Crater was formed by such an impact early in Martian history.
Lee cited orbital evidence that some areas of the rim were once hydrothermal systems with warm or hot groundwater.
“These areas may once have provided a warm, watery subsurface environment conducive to life,” he added. “Indeed, some paleontologists hypothesize that life on Earth began in such environments.”
The rover’s original mission envisaged just 12.4 miles (20 km) of driving. NASA recently approved an extension of its mission to explore the crater rim until roughly the end of 2028.
The rover’s plutonium-based power system is performing as expected, Lee said, adding it has “many years of useful energy still available.”
Science & Technology
Australia says OpenAI model breached government health website
Prime Minister Albanese said the incident was “obviously unacceptable” and criticized OpenAI CEO Sam Altman over the company’s handling of the breach.
Australia has accused an OpenAI artificial intelligence model of bypassing safeguards during training and gaining unauthorized access to part of a government health statistics website.
Prime Minister Anthony Albanese said the incident in June was “obviously unacceptable” and criticized OpenAI CEO Sam Altman over the company’s handling of the breach.
Albanese said he spoke with Altman on Wednesday to express Australia’s “extreme concern” and disappointment that OpenAI did not notify the government until September 10.
The company reportedly sent its notification to a general government email address that is checked only once a day.
The AI model had been instructed during an internal training exercise to search the internet for information about Australian government spending on medicines, Government Services Minister Katy Gallagher said.
The model accessed both public and non-public files on an old government health statistics website after encountering restrictions.
Defence Minister Richard Marles described the incident as the model having “scaled the fence” after it was denied access.
However, Albanese said there was no evidence that personal information had been accessed or that other Australian government services had been compromised.
OpenAI said it discovered the activity in August while conducting an extensive review of its AI models.
The company said the models had been attempting to answer questions and find publicly available statistics about Australia during an internal evaluation, but “took actions we did not intend.”
Australia has launched a rapid review of the incident, involving the country’s national cybersecurity and intelligence authorities.
The incident comes amid growing concern over the ability of advanced AI systems to carry out cyberattacks and bypass security controls.
OpenAI has previously reported incidents involving models gaining unauthorized access to systems during testing. Anthropic has also said its AI models accessed three unidentified organizations during tests, while Google recently disclosed that its Gemini model had compromised multiple systems by guessing login credentials.
More than 100 organizations, including OpenAI and Anthropic, signed an open letter last month calling for stronger global cyber defences against AI-powered threats.
Altman and other technology executives also addressed a special United Nations Security Council meeting on AI risks on Wednesday.
Tahawol: UN’s role in tackling global crises discsused
ACL: Arman FC rally late but fall 3–2 to Sorkh Poshan Khafi
Saar: Pakistan’s blame on Kabul for its own failures discussed
Toofan Herat secure narrow win over Ariana Khost in ACL season six
Switzerland cooperated with IEA to deport Afghan refugees: Report

Cricket Bonanza: Afghanistan set for packed international schedule

Afghanistan says 28 killed, 32 captured in Nuristan operation

Afghanistan on climate front line as Kabul faces groundwater warning

ACB announces Afghanistan squads for Bangladesh, Zimbabwe series

Trump rejects Iranian proposal to open Hormuz and end fighting
Tahawol: UN’s role in tackling global crises discsused
Saar: Pakistan’s blame on Kabul for its own failures discussed
Tawsia: New opportunities in Afghanistan’s energy, trade and agriculture sectors discussed
Exclusive interview with Ali Bilal, runner-up in Mr. Olympia Men’s Physique category

Tahawol: Doha meeting and Afghanistan’s political and economic future discussed
-
 Latest News3 days ago
Afghanistan’s new Wakhan road to China faces major hurdles
-
 Latest News5 days ago
Russian troops arrive in Uzbekistan for joint military exercises
-
 Latest News4 days ago
Qatar calls for shift from humanitarian aid to economic recovery in Afghanistan
-
 Latest News5 days ago
Trump blames migrants for violence in France as US midterms loom
-
 World4 days ago
Governments warn citizens over security risks in France after riots
-
 Science & Technology3 days ago
Governments take websites offline as critical cyber flaws trigger global alert
-
 Sport5 days ago
Arman FC begin second half of Afghanistan Champions League with 2-0 win
-
 Business4 days ago
Transit of Afghan goods through Sheikh Abu Nasr Farahi border crossing doubles