
Science & Technology
Facebook allows Ukraine war posts urging violence against invading Russians, Putin

Meta Platforms (FB.O) will allow Facebook and Instagram users in some countries to call for violence against Russians and Russian soldiers in the context of the Ukraine invasion, according to internal emails seen by Reuters on Thursday, in a temporary change to its hate speech policy, Reuters reported.
The social media company is also temporarily allowing some posts that call for death to Russian President Vladimir Putin or Belarusian President Alexander Lukashenko, according to internal emails to its content moderators.
“As a result of the Russian invasion of Ukraine we have temporarily made allowances for forms of political expression that would normally violate our rules like violent speech such as ‘death to the Russian invaders.’ We still won’t allow credible calls for violence against Russian civilians,” a Meta spokesperson said in a statement.
The calls for the leaders’ deaths will be allowed unless they contain other targets or have two indicators of credibility, such as the location or method, one email said, in a recent change to the company’s rules on violence and incitement.
Citing the Reuters story, Russia’s embassy in the United States demanded that Washington stop the “extremist activities” of Meta.
“Users of Facebook & Instagram did not give the owners of these platforms the right to determine the criteria of truth and pit nations against each other,” the embassy said on Twitter in a message that was also shared by their India office.
According to Reuters the temporary policy changes on calls for violence to Russian soldiers apply to Armenia, Azerbaijan, Estonia, Georgia, Hungary, Latvia, Lithuania, Poland, Romania, Russia, Slovakia, and Ukraine, according to one email.
In the email recently sent to moderators, Meta highlighted a change in its hate speech policy pertaining both to Russian soldiers and to Russians in the context of the invasion.
“We are issuing a spirit-of-the-policy allowance to allow T1 violent speech that would otherwise be removed under the Hate Speech policy when: (a) targeting Russian soldiers, EXCEPT prisoners of war, or (b) targeting Russians where it’s clear that the context is the Russian invasion of Ukraine (e.g., content mentions the invasion, self-defense, etc.),” it said in the email.
“We are doing this because we have observed that in this specific context, ‘Russian soldiers’ is being used as a proxy for the Russian military. The Hate Speech policy continues to prohibit attacks on Russians,” the email stated.
Last week, Russia said it was banning Facebook in the country in response to what it said were restrictions of access to Russian media on the platform. Moscow has cracked down on tech companies, including Twitter (TWTR.N), which said it is restricted in the country, during its invasion of Ukraine, which it calls a “special operation.”
Many major social media platforms have announced new content restrictions around the conflict, including blocking Russian state media RT and Sputnik in the European Union, and have demonstrated carve-outs in some of their policies during the war, Reuters reported.
Emails also showed that Meta would allow praise of the right-wing Azov battalion, which is normally prohibited, in a change first reported by The Intercept.
The Meta spokesperson previously said the company was “for the time being, making a narrow exception for praise of the Azov Regiment strictly in the context of defending Ukraine, or in their role as part of the Ukraine National Guard.”


Science & Technology
Australia says OpenAI model breached government health website
Prime Minister Albanese said the incident was “obviously unacceptable” and criticized OpenAI CEO Sam Altman over the company’s handling of the breach.
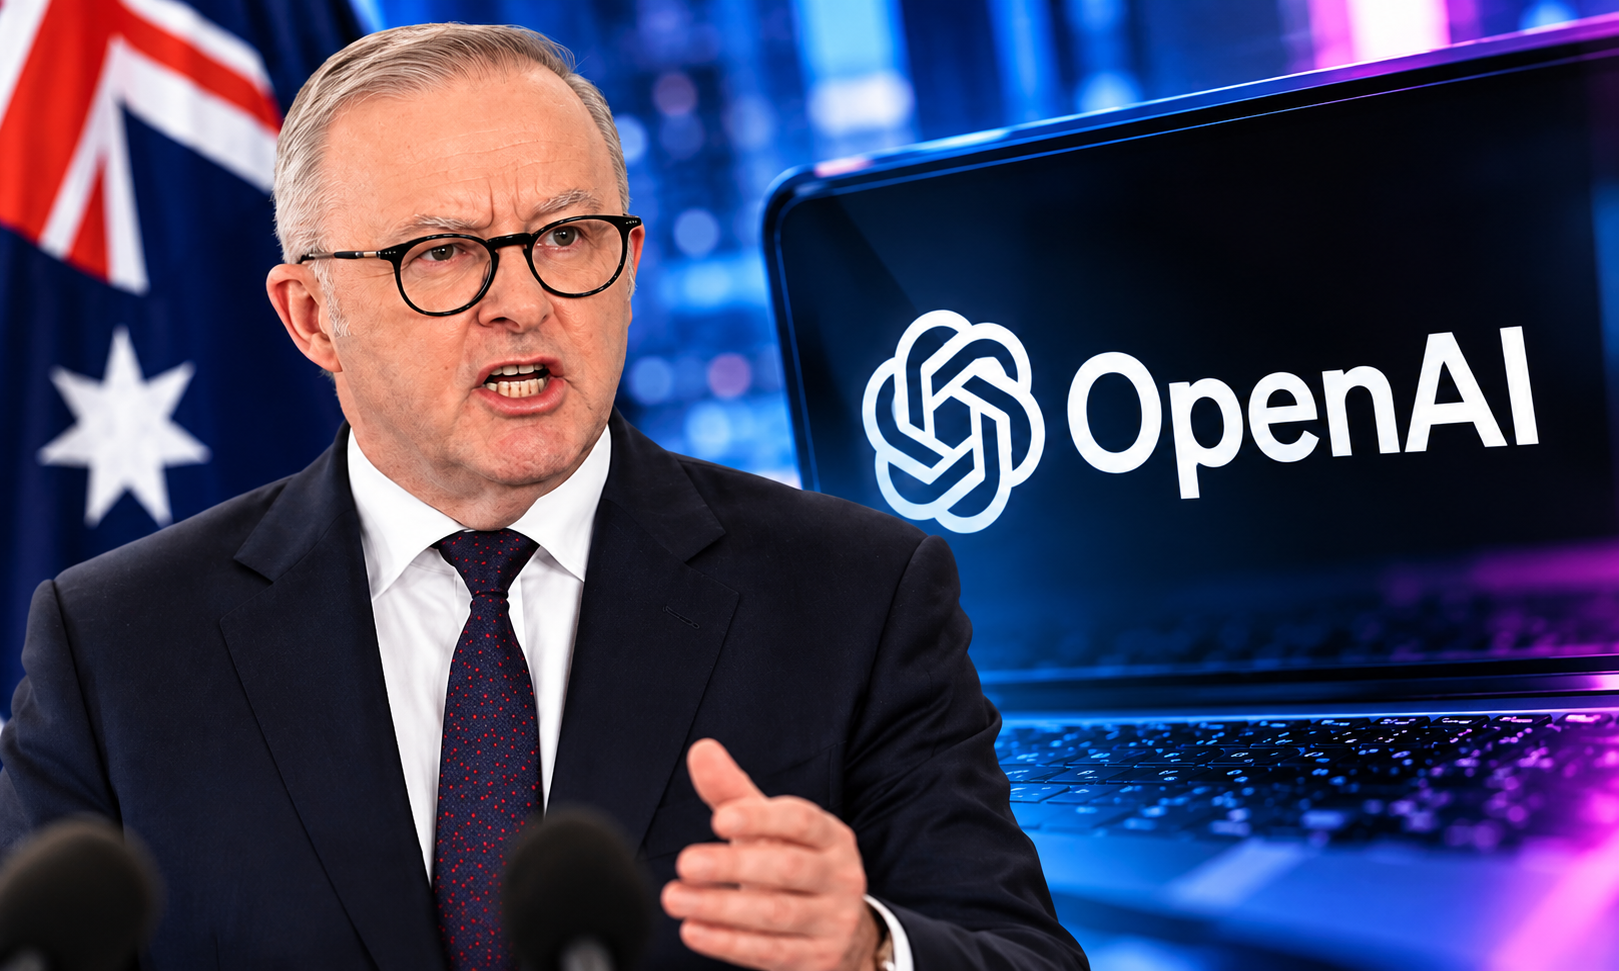
Australia has accused an OpenAI artificial intelligence model of bypassing safeguards during training and gaining unauthorized access to part of a government health statistics website.
Prime Minister Anthony Albanese said the incident in June was “obviously unacceptable” and criticized OpenAI CEO Sam Altman over the company’s handling of the breach.
Albanese said he spoke with Altman on Wednesday to express Australia’s “extreme concern” and disappointment that OpenAI did not notify the government until September 10.
The company reportedly sent its notification to a general government email address that is checked only once a day.
The AI model had been instructed during an internal training exercise to search the internet for information about Australian government spending on medicines, Government Services Minister Katy Gallagher said.
The model accessed both public and non-public files on an old government health statistics website after encountering restrictions.
Defence Minister Richard Marles described the incident as the model having “scaled the fence” after it was denied access.
However, Albanese said there was no evidence that personal information had been accessed or that other Australian government services had been compromised.
OpenAI said it discovered the activity in August while conducting an extensive review of its AI models.
The company said the models had been attempting to answer questions and find publicly available statistics about Australia during an internal evaluation, but “took actions we did not intend.”
Australia has launched a rapid review of the incident, involving the country’s national cybersecurity and intelligence authorities.
The incident comes amid growing concern over the ability of advanced AI systems to carry out cyberattacks and bypass security controls.
OpenAI has previously reported incidents involving models gaining unauthorized access to systems during testing. Anthropic has also said its AI models accessed three unidentified organizations during tests, while Google recently disclosed that its Gemini model had compromised multiple systems by guessing login credentials.
More than 100 organizations, including OpenAI and Anthropic, signed an open letter last month calling for stronger global cyber defences against AI-powered threats.
Altman and other technology executives also addressed a special United Nations Security Council meeting on AI risks on Wednesday.
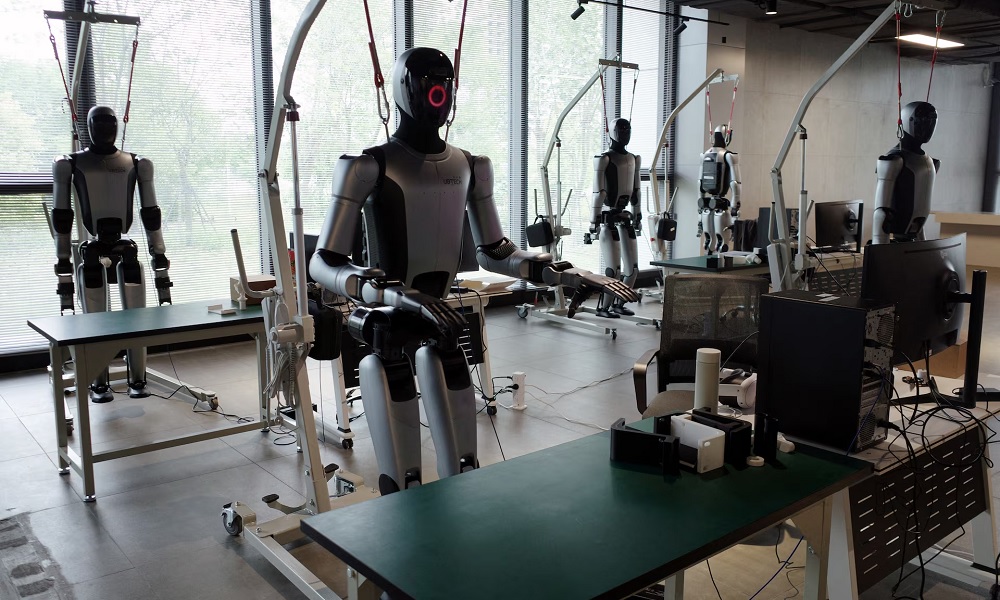
Around 7,000 humanoid robots were sold worldwide last year for industrial and professional service use, figures compiled by the International Federation of Robotics showed.
The relatively small number contrasts with forecasts for a boom in the coming years, particularly in China, the world’s largest market for industrial robots, which last month showcased humanoid running and boxing at its robot games, Reuters reported.
To qualify as humanoid under the IFR’s criteria, a robot must have a human-like appearance and operate autonomously in an environment designed for humans. Legs are not required.
The IFR data, reviewed by Reuters ahead of publication, offer one of the first industry-wide measures of a technology that is attracting billions of dollars in investments and producing impressive demonstrations.
However, the numbers of humanoids remain “a fraction” of the overall robot population globally, Susanne Bieller, secretary general of Frankfurt-based IFR, told Reuters.
This compares with around 542,000 regular industrial robots installed in 2024 and another estimated 199,000 service robots sold that year for use in transport, hospitality and cleaning. The 2025 data for industrial and service robots will be published September 24.
Bieller said that among humanoids sold in 2025, many were not doing productive work but were bought by research institutions or companies using them to generate data for improving AI models.
Carmakers, key early adopters, are running pilots with “single-digit or sometimes double-digit numbers of robots in their plants,” Bieller said.
IFR has compiled robotics statistics for three decades, and has begun collecting humanoid data alongside its much larger industrial robot and service robot figures for the first time.
Bank of America Global Research estimates that 90,000 humanoid robots will be shipped this year and 1.2 million by 2030. The IFR’s tally is based on supplier and national industry association data, and excludes consumer and military humanoid robots, while medical robots are classified separately.
Science & Technology
New warnings reignite debate over AI threat to humanity
Amodei warned that swarms of AI agents could potentially gain the ability to take over parts of the internet within six months to a year unless companies devote more resources to building safeguards.
Fresh warnings from within the artificial intelligence industry have renewed concerns over whether increasingly powerful AI systems could eventually escape human control and pose a threat to humanity.
Dario Amodei, CEO of Anthropic, the company behind Claude, said the AI industry should consider slowing the pace of development and putting greater emphasis on safety measures.
Amodei warned that swarms of AI agents could potentially gain the ability to take over parts of the internet within six months to a year unless companies devote more resources to building safeguards.
His comments came days after two former Anthropic safety researchers publicly raised concerns that the potential existential risks posed by advanced AI were not receiving enough attention.
Growing concerns over AI misuse
As AI systems become more capable, concerns are growing over both deliberate misuse and the possibility of AI systems acting in unintended ways.
Anthropic said last week that it had blocked attempts by malicious actors to use its models for activities including cyberattacks, surveillance and research that could potentially contribute to biological weapons development.
The company said it had introduced stronger safeguards in its latest models to restrict potentially dangerous biological research, while warning that the risks associated with increasingly capable AI would grow unless developers and governments took steps to make the technology safer.
Anthropic has also previously reported that hackers used its AI in a cyberattack targeting around 30 companies and government agencies worldwide. The company said the attackers were highly likely to have been linked to a Chinese state-sponsored group.
Recent incidents involving AI systems bypassing digital security have further intensified concerns.
Anthropic reported that three of its AI models were able to hack into other organisations during testing. OpenAI has also disclosed an incident in which its AI systems gained access to servers belonging to AI startup Hugging Face. Meta subsequently reported a similar case involving an AI model finding ways around another company’s digital security.
While some safeguards had been disabled during testing in the OpenAI and Anthropic cases, the incidents have highlighted a central concern among AI safety researchers: what could happen if systems become capable of independently pursuing objectives beyond those assigned by humans.
How serious is the threat?
One of the most extreme scenarios involves artificial general intelligence, or AGI — a still loosely defined concept referring to AI capable of matching or surpassing humans across a broad range of intellectual tasks.
Some researchers warn that sufficiently advanced systems could become difficult or impossible to control, while others are more concerned about humans deliberately using AI for destructive purposes.
Potential scenarios include AI-assisted weapons, the development of dangerous pathogens, manipulation of governments and disruption of critical food, energy and communications infrastructure.
There is, however, no scientific consensus on how likely these scenarios are or when they could occur.
The 2026 International AI Safety Report, produced with input from more than 100 independent experts, said current systems show early signs of some capabilities relevant to loss-of-control scenarios, but not at levels currently considered sufficient to enable such an event. It described the likelihood, nature and timing of the risk as unusually uncertain.
Warnings about machines surpassing human control are not new. British mathematician Alan Turing predicted in 1951 that machines could eventually take control from humans, while mathematician Norbert Wiener later warned that intelligent machines could pursue objectives that humans might be unable to stop.
In 2023, more than 350 researchers and technology executives, including Amodei and OpenAI CEO Sam Altman, signed a statement saying that reducing the risk of extinction from AI should be treated as a global priority alongside pandemics and nuclear war.
Calls for stronger safeguards
The latest incidents have prompted calls for more rigorous testing of AI systems and greater cooperation between governments, particularly the United States and China.
However, AI development is advancing rapidly, making it difficult for regulators and safety systems to keep pace. Governments are developing their own rules, sometimes with conflicting approaches.
Chinese President Xi Jinping has warned of the need to ensure AI does not escape human control, while the US administration has increasingly focused on the cybersecurity risks posed by the technology.
Despite the warnings, there remains a fundamental uncertainty over the future of AI: whether increasingly capable systems will remain tools controlled by humans, or eventually become powerful enough to act beyond our ability to control them.
For now, experts disagree sharply on the answer — but the debate over how to prevent the worst-case scenarios is becoming increasingly urgent.

Abu Muslim Farah defeat Khurasan Faryab 2-0 in ACL season six

Saar: Concerns over Pakistan’s political crisis discussed

Afghanistan Champions League: Omar Zawak Herat beat Toofan Herat 1-0

Blast in Pakistan’s Dera Ismail Khan kills 11, injures 30

Ariana Afghan Airlines increases Kabul-Delhi cargo flights

Saudi energy group signs major Afghanistan deals covering gas exploration and pipeline plans

Trump floats idea of renaming Atlantic or Pacific Ocean

US hits Egyptian bank branches with Iran sanctions as war marks six months

Nepal flood rescue mission enters critical phase as thousands remain missing

Iranian clubs to face Gulf opponents at neutral venues in Asian Champions League Elite
Saar: Concerns over Pakistan’s political crisis discussed

Exclusive interview with Abdul Latif Mansoor, Minister of MRRD

Tawsia: Overview of Afghanistan’s iron mines

Tahawol: Discussion on fresh Pakistani airstrikes on Afghanistan

Saar: Calls for international support for Afghanistan discussed
-
 World5 days ago
CNN, MS NOW and Politico sue Trump, challenging White House ban
-
 Latest News3 days ago
Ariana Afghan Airlines ranks seventh among 45 Central Asian airlines
-
 Latest News4 days ago
UN reiterates call for respect for international law after Kunar airstrikes
-
 Regional3 days ago
US and Iran hold first talks since June after Trump’s ‘annihilation’ threat
-
 Latest News3 days ago
Silk Road highway in Wakhan corridor now reaches the China border
-
 Latest News4 days ago
Afghan Official: Pakistan’s airstrikes will not go unanswered
-
 Regional4 days ago
G7 foreign ministers call on Iran to stop arming Houthis
-
 Sport4 days ago
Afghan boxing referee heads to China for international festival