
Science & Technology
North Korea fires likely submarine-launched ballistic missile, South Korea military says


North Korea fired a ballistic missile on Saturday (May 7), South Korea’s military said, three days before the inauguration of South Korean president-elect Yoon Suk-yeol, who has vowed to take a hard line against the North.
South Korea’s military said that North Korea fired what is believed to be a submarine-launched ballistic missile (SLBM) into the sea off its east coast around 0507 GMT on Saturday from around Sinpo, where North Korea keeps submarines as well as equipment for test-firing SLBMs. Japan’s defence ministry also tweeted that the projectile could be a ballistic missile. Japanese public broadcaster NHK, citing government sources, said the projectile landed outside Japan’s exclusive economic zone.
On Wednesday (May 4), North Korea fired a ballistic missile toward the sea off its east coast, South Korea and Japan said, after Pyongyang vowed to develop its nuclear forces “at the fastest possible speed”. The United States assessed that North Korea was preparing its Punggye-ri nuclear test site and could be ready to conduct a test there as early as this month.
Yoon takes office on Tuesday. U.S. President Joe Biden is to visit South Korea and meet with him on May 21.
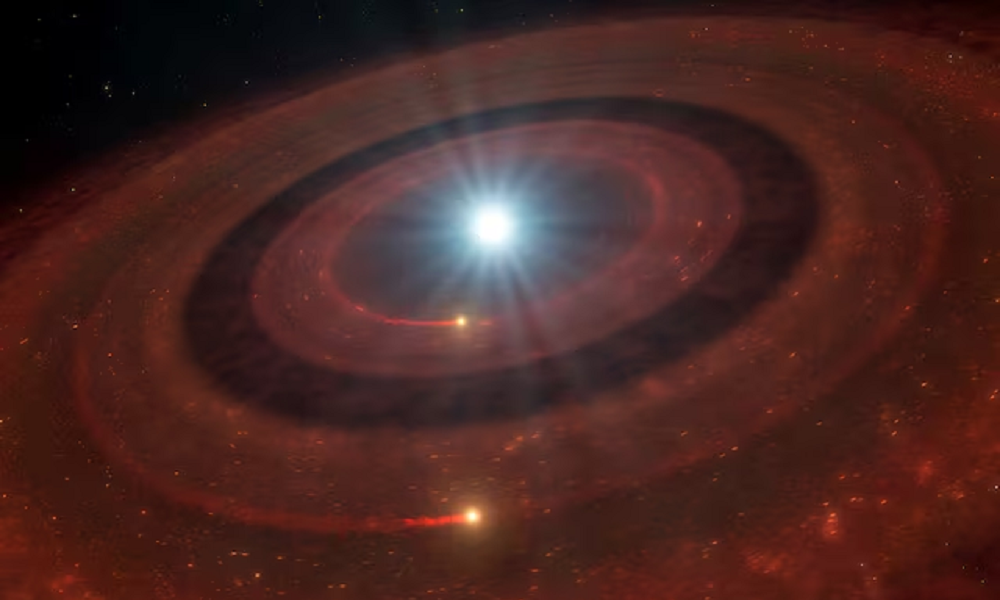
Astronomers have discovered a white dwarf star surrounded by two distinct rings of planetary debris, offering new insights into what may happen to planetary systems, including our own, when their host stars reach the end of their lives.
The star, identified as J1328−1450, is located about 1,600 light-years from Earth in the constellation Virgo. Observations made using the European Southern Observatory’s Very Large Telescope in Chile revealed an unusual arrangement of dust and gas around the star.
According to researchers, the debris appears to form two separate rings, a structure not previously observed around any of the 21 white dwarfs known to have surrounding planetary debris.
The scientists believe that two relatively large rocky bodies may have survived the star’s transformation into a white dwarf and could be responsible for shaping the surrounding material. One of these objects may be roughly the size of Pluto, while the other is smaller.
Researchers say the discovery provides further evidence that some rocky planetary bodies can survive the dramatic changes that occur when a star exhausts its fuel and expands into a red giant.
The findings, published in the journal *Nature Astronomy*, suggest that the original star may once have hosted a planetary system. During its expansion, it likely engulfed some of its innermost planets, while more distant objects survived.
Over time, gravitational forces may have pulled some of these surviving bodies closer to the white dwarf, tearing them apart and scattering their material into surrounding rings of dust and gas.
Astronomers also found differences in the chemical composition of the two rings, particularly in their magnesium content, suggesting that they may have originated from different rocky bodies or from different layers of a disrupted object.
The discovery could offer a glimpse into the distant future of our own solar system. Scientists estimate that in about five billion years, the Sun will expand into a red giant before shedding its outer layers and becoming a white dwarf.
During this process, Mercury and Venus are expected to be engulfed, while the fate of Earth remains uncertain. More distant planets, including Jupiter and Saturn, are expected to have a greater chance of surviving.
Researchers say that, after the Sun becomes a white dwarf, surviving planets, moons and asteroids could also be pulled towards it and broken apart by its intense gravitational force.
They suggest that the newly observed system may represent one possible stage in the far-distant future of our solar system.
Science & Technology
Binance says it has covered $6 billion of $6.3 billion stolen in hack
The US Federal Bureau of Investigation (FBI) said on Saturday the North Korean state-sponsored unit known as TraderTraitor was responsible for the attack.
Binance, the world’s biggest cryptocurrency exchange, said it has covered $6 billion of the $6.3 billion stolen from its platform by using company money to buy replacement tokens, after a hack that US officials said was carried out by a North Korean state-sponsored unit known as TraderTraitor.
“We had already covered $6B of the impacted amount of the hacked loss,” Binance said on X on Saturday, after saying earlier that it had covered 90% of the stolen funds, Reuters reported.
The remaining amount, now less than 10%, consists of assets that are less liquid and may take longer to source in the required amounts, according to Binance.
The US Federal Bureau of Investigation (FBI) said on Saturday the North Korean state-sponsored unit known as TraderTraitor was responsible for the attack.
North Korea has for years denied using state-linked cyber units for espionage, financial theft and revenue. Its mission in Geneva and embassy in China did not respond to requests for comment.
Members of the unit were observed by law enforcement converting stolen assets into the cryptocurrency ethereum, the FBI said in a statement, adding that it expects “further laundering” of the assets through the use of related technology.
Analysts had previously blamed North Korea and said it could be the largest financial heist of all time.
Binance has been working with industry partners to freeze some of the affected assets, with about $3 billion located as of Friday.
The company has repeatedly said it would bear the financial impact of the funds stolen in the hack.
The money spent re-buying tokens came from using part of its $1 billion Secure Asset Fund for Users (SAFU), a bitcoin reserve it holds to protect customers in the event of security breaches, as well as some of its Futures Insurance Fund, and the company’s own corporate treasury, it said on X.
Co-CEO Yi He said on Saturday that 50% of its SAFU funds would be used, while the company said it was committing to replenishing the fund to return it to about $1 billion.
Crypto prices fell on Friday, while Binance sought to reassure customers that their funds were safe after the hack.
Co-CEO Richard Teng had said that the breach was a “complex attack” involving a compromised laptop and malicious software designed to delete evidence of its activity, making it harder to trace and investigate.
After the hack, the exchange stopped allowing customers to withdraw their funds, but it said on Saturday it was still on track to reopen withdrawals on Sunday.
Withdrawals were not open as of 02:50 GMT on Sunday.
Binance said it has set aside around $6.34 billion of company funds internally to cover the losses.
Binance also said it had taken a new snapshot of assets held on its platform as of 0000 GMT on October 31, as part of its proof-of-reserves process.
Users holding the 10 listed tokens — BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, and ZEC — would be able to verify that their assets were backed at a minimum ratio of 1:1 once the full proof was available, it said.
Science & Technology
Governments take websites offline as critical cyber flaws trigger global alert
Security patches were released prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
Governments and organisations across Europe and beyond have taken websites and online services offline after the discovery of two critical vulnerabilities in widely used web software triggered an international cyber-security alert.
The vulnerabilities affect PHP, a programming language used extensively to operate websites and online applications. Attackers could potentially exploit the flaws to execute malicious code remotely on vulnerable servers, threatening sensitive information and digital infrastructure.
Security patches were released on Wednesday, October 21, prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
The Netherlands, Finland, France, Belgium and Germany have also reported precautionary shutdowns affecting government websites and other public-facing services.
In the Netherlands, affected platforms included Overheid.nl, MijnOverheid.nl and DigiD. The country’s National Cyber Security Centre also temporarily took its own website offline.
Finland’s state IT services provider, Valtori, suspended public government web services as a precaution, while France’s Interior Ministry temporarily took the websites of local administrative authorities offline.
In Belgium, the Foreign Ministry took its websites offline amid concerns about potential exploitation, although the country’s cybersecurity centre said it had not observed attacks on Belgian websites at the time.
Germany’s federal IT service provider also temporarily disabled several websites, with officials saying the measure was precautionary and no security incidents were known to have occurred.
The disruption extended beyond government agencies. Websites and online services belonging to hospitals, educational platforms and other organisations were also affected, highlighting the potential reach of vulnerabilities in widely deployed software.
In Australia, the Australian Cyber Security Centre’s website, cyber.gov.au, was among the government services affected by the security alert. Australian authorities said they were not aware of active exploitation of the vulnerabilities.
In the United States, the National Security Agency and other cybersecurity authorities urged organisations to prepare for immediate updates and take vulnerable systems offline if they could not be secured promptly. The Wikimedia Foundation, which operates Wikipedia, also took some systems offline as a precaution while addressing the flaws.
Cybersecurity company Cloudflare reported seeing early attacks associated with the vulnerabilities, although reports of exploitation do not establish that every affected organisation suffered a breach.
The incident highlights the risks created by the internet’s reliance on shared software. PHP is used across a substantial proportion of websites, meaning a single vulnerability can affect organisations in multiple countries and sectors simultaneously.
Security specialists have urged website operators to identify affected systems, install the relevant patches and examine server logs for signs of unauthorised access. Applying an update may prevent further exploitation, but organisations must also investigate whether attackers gained access before their systems were secured.
Authorities have not established that all affected websites were breached. The precautionary shutdowns are intended to reduce exposure while administrators apply fixes and verify that their systems are safe to restore.
The alert has underscored the challenge facing governments and businesses in responding to critical software vulnerabilities that can rapidly become an international security concern.
Saar: Afghanistan’s declining humanitarian aid funding discussed
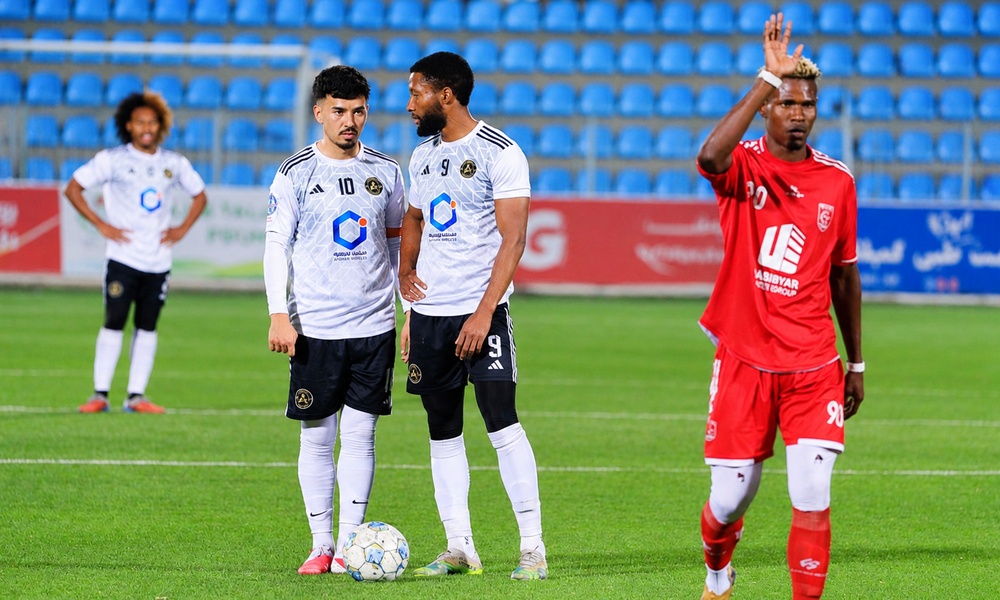
Toofan Herat defeat Arman FC 2–0 in Afghanistan Champions League
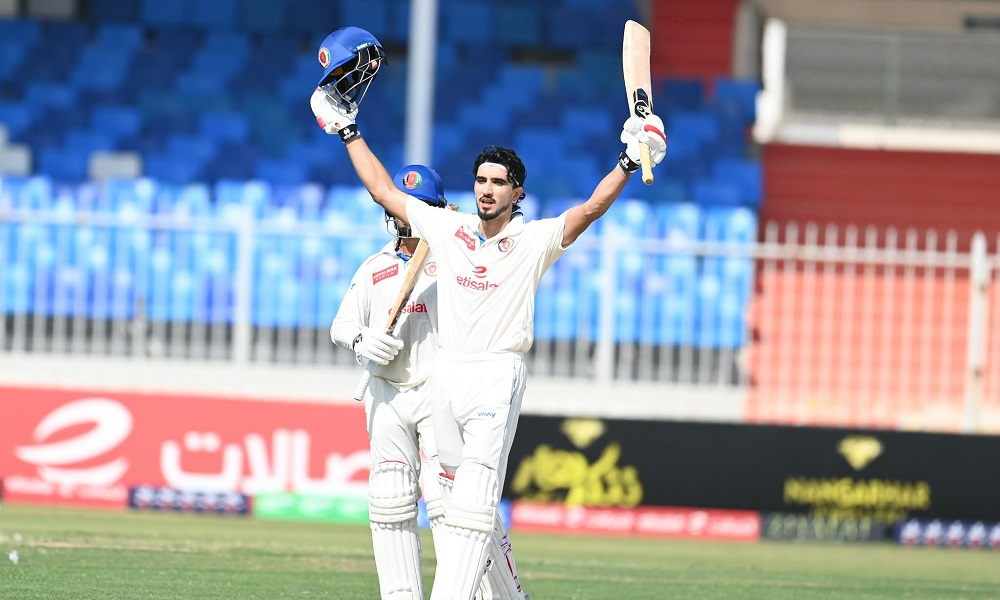
Afghanistan trail Zimbabwe by 102 runs at stumps on day three of first Test
Astronomers discover white dwarf surrounded by two rings of planetary debris
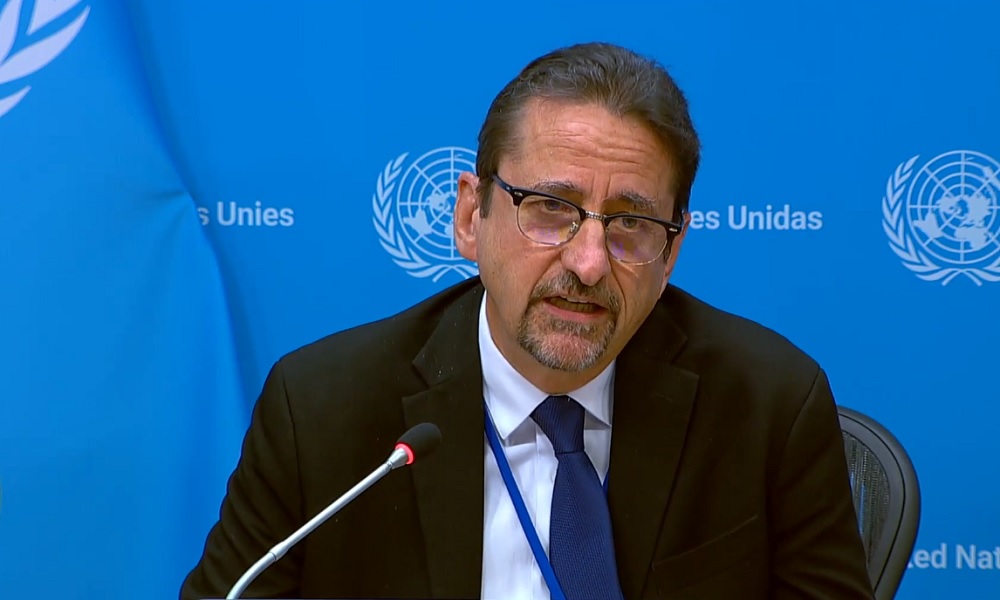
UN official warns Afghanistan’s humanitarian crisis could threaten regional stability and security

Afghanistan finish runners-up after 6-0 defeat to Brazil in futsal final

Trump says US will not attack Iran before midterm elections in November

Trump says US may strike Iran’s ‘Pickaxe Mountain’ nuclear facility

Afghan futsal coach: Brazil tournament is first step towards new goals and World Cup

WHO calls for greater mental health support in Afghanistan
Saar: Afghanistan’s declining humanitarian aid funding discussed
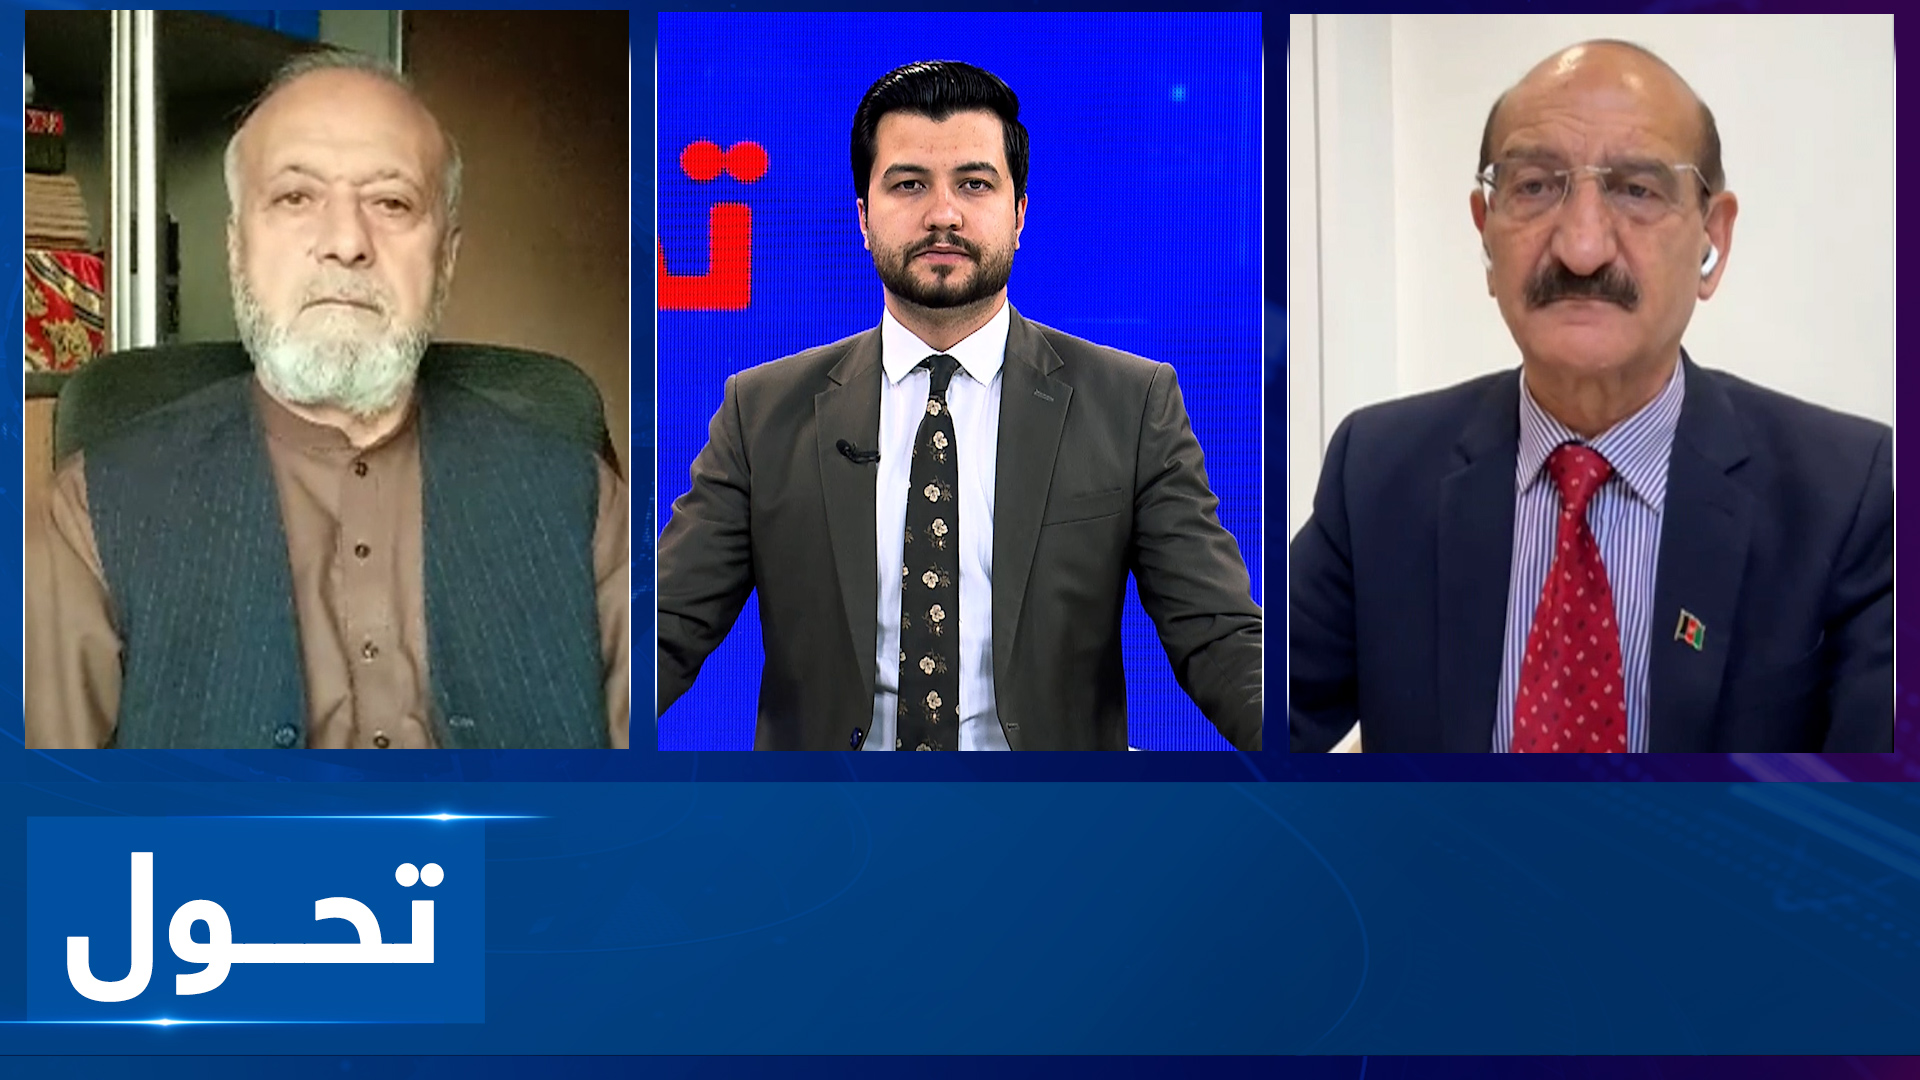
Tahawol: Calls for stronger joint action against terrorism discussed
Saar: Impact of closing trade routes between Kabul-Pakistan discussed
El-Sayed’s historic victory opens a new chapter for Muslim Americans
Tahawol: Russia’s Moscow Format for Afghan issues discussed
-
 Sport5 days ago
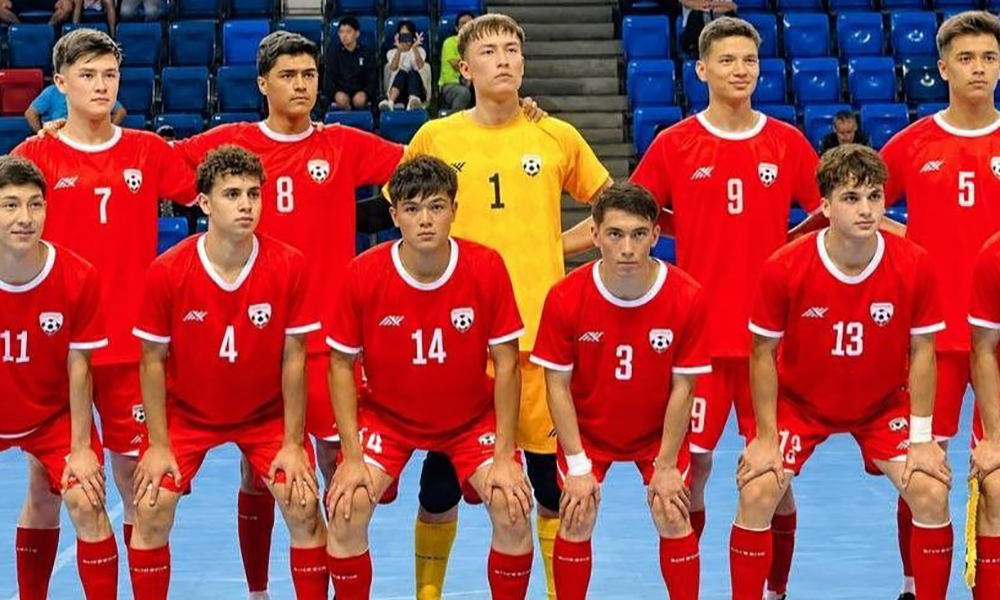
Afghanistan futsal team thrash Panama 5-0 in flying start to Dakar Youth Olympics
-
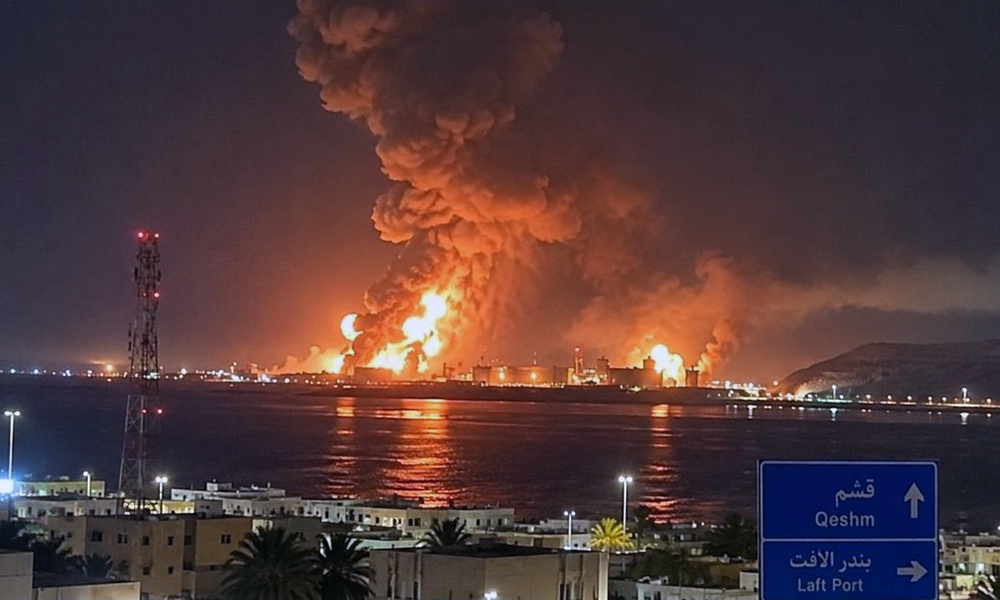 World5 days ago
US carries out ‘defensive’ strikes on Iran’s Qeshm Island, officials say
-
 Sport2 days ago
Afghanistan suffer narrow defeat against Argentina at Dakar Youth Olympics
-
 Regional4 days ago
Iran says contacts over ending war continue after talks finish with no breakthrough
-
 Latest News4 days ago
Iran plans new four-nation meeting on Afghanistan amid regional diplomatic efforts
-
 Latest News3 days ago
US judge temporarily blocks deportation of detained Afghans
-

 Latest News4 days ago
US lawmakers urge Trump administration to halt Afghan deportations
-
 Climate Change3 days ago
IEA to attend UN climate summit for second time since returning to power