
Science & Technology
International astronaut will be invited on future NASA moon landing


An international astronaut will join U.S. astronauts on the moon by decade’s end under an agreement announced Wednesday by NASA and the White House.
The news came as Vice President Kamala Harris convened a meeting in Washington of the National Space Council, the third such gathering under the Biden administration, AP reported.
There was no mention of who the international moonwalker might be or even what country would be represented. A NASA spokeswoman later said that crews would be assigned closer to the lunar-landing missions, and that no commitments had yet been made to another country.
NASA has included international astronauts on trips to space for decades. Canadian Jeremy Hansen will fly around the moon a year or so from now with three U.S. astronauts.
Another crew would actually land; it would be the first lunar touchdown by astronauts in more than a half-century. That’s not likely to occur before 2027, according to the U.S. Government Accountability Office.
All 12 moonwalkers during NASA’s Apollo program of the 1960s and 1970s were U.S. citizens. The space agency’s new moon exploration program is named Artemis after Apollo’s mythological twin sister.
Including international partners “is not only sincerely appreciated, but it is urgently needed in the world today,” Hansen told the council.
NASA has long stressed the need for global cooperation in space, establishing the Artemis Accords along with the U.S. State Department in 2020 to promote responsible behavior not just at the moon but everywhere in space. Representatives from all 33 countries that have signed the accords so far were expected at the space council’s meeting in Washington.
“We know from experience that collaboration on space delivers,” said Secretary of State Antony Blinken, citing the Webb Space Telescope, a U.S., European and Canadian effort.
Notably missing from the Artemis Accords: Russia and China, the only countries besides the U.S. to launch their own citizens into orbit. Russia is a partner with NASA in the International Space Station, along with Europe, Japan and Canada. Even earlier in the 1990s, the Russian and U.S. space agencies teamed up during the shuttle program to launch each other’s astronauts to Russia’s former orbiting Mir station.
During Wednesday’s meeting, Harris also announced new policies to ensure the safe use of space as more and more private companies and countries aim skyward. Among the issues that the U.S. is looking to resolve: the climate crisis and the growing amount of space junk around Earth. A 2021 anti-satellite missile test by Russia added more than 1,500 pieces of potentially dangerous orbiting debris, and Blinken joined others at the meeting in calling for all nations to end such destructive testing.



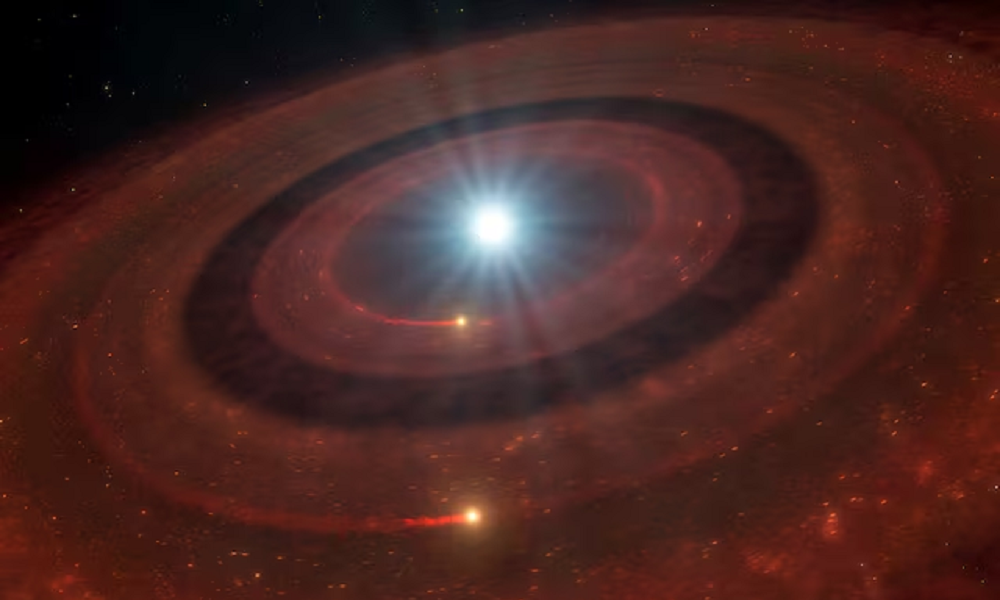
Astronomers have discovered a white dwarf star surrounded by two distinct rings of planetary debris, offering new insights into what may happen to planetary systems, including our own, when their host stars reach the end of their lives.
The star, identified as J1328−1450, is located about 1,600 light-years from Earth in the constellation Virgo. Observations made using the European Southern Observatory’s Very Large Telescope in Chile revealed an unusual arrangement of dust and gas around the star.
According to researchers, the debris appears to form two separate rings, a structure not previously observed around any of the 21 white dwarfs known to have surrounding planetary debris.
The scientists believe that two relatively large rocky bodies may have survived the star’s transformation into a white dwarf and could be responsible for shaping the surrounding material. One of these objects may be roughly the size of Pluto, while the other is smaller.
Researchers say the discovery provides further evidence that some rocky planetary bodies can survive the dramatic changes that occur when a star exhausts its fuel and expands into a red giant.
The findings, published in the journal *Nature Astronomy*, suggest that the original star may once have hosted a planetary system. During its expansion, it likely engulfed some of its innermost planets, while more distant objects survived.
Over time, gravitational forces may have pulled some of these surviving bodies closer to the white dwarf, tearing them apart and scattering their material into surrounding rings of dust and gas.
Astronomers also found differences in the chemical composition of the two rings, particularly in their magnesium content, suggesting that they may have originated from different rocky bodies or from different layers of a disrupted object.
The discovery could offer a glimpse into the distant future of our own solar system. Scientists estimate that in about five billion years, the Sun will expand into a red giant before shedding its outer layers and becoming a white dwarf.
During this process, Mercury and Venus are expected to be engulfed, while the fate of Earth remains uncertain. More distant planets, including Jupiter and Saturn, are expected to have a greater chance of surviving.
Researchers say that, after the Sun becomes a white dwarf, surviving planets, moons and asteroids could also be pulled towards it and broken apart by its intense gravitational force.
They suggest that the newly observed system may represent one possible stage in the far-distant future of our solar system.
Science & Technology
Binance says it has covered $6 billion of $6.3 billion stolen in hack
The US Federal Bureau of Investigation (FBI) said on Saturday the North Korean state-sponsored unit known as TraderTraitor was responsible for the attack.
Binance, the world’s biggest cryptocurrency exchange, said it has covered $6 billion of the $6.3 billion stolen from its platform by using company money to buy replacement tokens, after a hack that US officials said was carried out by a North Korean state-sponsored unit known as TraderTraitor.
“We had already covered $6B of the impacted amount of the hacked loss,” Binance said on X on Saturday, after saying earlier that it had covered 90% of the stolen funds, Reuters reported.
The remaining amount, now less than 10%, consists of assets that are less liquid and may take longer to source in the required amounts, according to Binance.
The US Federal Bureau of Investigation (FBI) said on Saturday the North Korean state-sponsored unit known as TraderTraitor was responsible for the attack.
North Korea has for years denied using state-linked cyber units for espionage, financial theft and revenue. Its mission in Geneva and embassy in China did not respond to requests for comment.
Members of the unit were observed by law enforcement converting stolen assets into the cryptocurrency ethereum, the FBI said in a statement, adding that it expects “further laundering” of the assets through the use of related technology.
Analysts had previously blamed North Korea and said it could be the largest financial heist of all time.
Binance has been working with industry partners to freeze some of the affected assets, with about $3 billion located as of Friday.
The company has repeatedly said it would bear the financial impact of the funds stolen in the hack.
The money spent re-buying tokens came from using part of its $1 billion Secure Asset Fund for Users (SAFU), a bitcoin reserve it holds to protect customers in the event of security breaches, as well as some of its Futures Insurance Fund, and the company’s own corporate treasury, it said on X.
Co-CEO Yi He said on Saturday that 50% of its SAFU funds would be used, while the company said it was committing to replenishing the fund to return it to about $1 billion.
Crypto prices fell on Friday, while Binance sought to reassure customers that their funds were safe after the hack.
Co-CEO Richard Teng had said that the breach was a “complex attack” involving a compromised laptop and malicious software designed to delete evidence of its activity, making it harder to trace and investigate.
After the hack, the exchange stopped allowing customers to withdraw their funds, but it said on Saturday it was still on track to reopen withdrawals on Sunday.
Withdrawals were not open as of 02:50 GMT on Sunday.
Binance said it has set aside around $6.34 billion of company funds internally to cover the losses.
Binance also said it had taken a new snapshot of assets held on its platform as of 0000 GMT on October 31, as part of its proof-of-reserves process.
Users holding the 10 listed tokens — BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, and ZEC — would be able to verify that their assets were backed at a minimum ratio of 1:1 once the full proof was available, it said.
Science & Technology
Governments take websites offline as critical cyber flaws trigger global alert
Security patches were released prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
Governments and organisations across Europe and beyond have taken websites and online services offline after the discovery of two critical vulnerabilities in widely used web software triggered an international cyber-security alert.
The vulnerabilities affect PHP, a programming language used extensively to operate websites and online applications. Attackers could potentially exploit the flaws to execute malicious code remotely on vulnerable servers, threatening sensitive information and digital infrastructure.
Security patches were released on Wednesday, October 21, prompting authorities to urge organisations to update affected systems immediately or take vulnerable services offline until they could be secured.
The Netherlands, Finland, France, Belgium and Germany have also reported precautionary shutdowns affecting government websites and other public-facing services.
In the Netherlands, affected platforms included Overheid.nl, MijnOverheid.nl and DigiD. The country’s National Cyber Security Centre also temporarily took its own website offline.
Finland’s state IT services provider, Valtori, suspended public government web services as a precaution, while France’s Interior Ministry temporarily took the websites of local administrative authorities offline.
In Belgium, the Foreign Ministry took its websites offline amid concerns about potential exploitation, although the country’s cybersecurity centre said it had not observed attacks on Belgian websites at the time.
Germany’s federal IT service provider also temporarily disabled several websites, with officials saying the measure was precautionary and no security incidents were known to have occurred.
The disruption extended beyond government agencies. Websites and online services belonging to hospitals, educational platforms and other organisations were also affected, highlighting the potential reach of vulnerabilities in widely deployed software.
In Australia, the Australian Cyber Security Centre’s website, cyber.gov.au, was among the government services affected by the security alert. Australian authorities said they were not aware of active exploitation of the vulnerabilities.
In the United States, the National Security Agency and other cybersecurity authorities urged organisations to prepare for immediate updates and take vulnerable systems offline if they could not be secured promptly. The Wikimedia Foundation, which operates Wikipedia, also took some systems offline as a precaution while addressing the flaws.
Cybersecurity company Cloudflare reported seeing early attacks associated with the vulnerabilities, although reports of exploitation do not establish that every affected organisation suffered a breach.
The incident highlights the risks created by the internet’s reliance on shared software. PHP is used across a substantial proportion of websites, meaning a single vulnerability can affect organisations in multiple countries and sectors simultaneously.
Security specialists have urged website operators to identify affected systems, install the relevant patches and examine server logs for signs of unauthorised access. Applying an update may prevent further exploitation, but organisations must also investigate whether attackers gained access before their systems were secured.
Authorities have not established that all affected websites were breached. The precautionary shutdowns are intended to reduce exposure while administrators apply fixes and verify that their systems are safe to restore.
The alert has underscored the challenge facing governments and businesses in responding to critical software vulnerabilities that can rapidly become an international security concern.
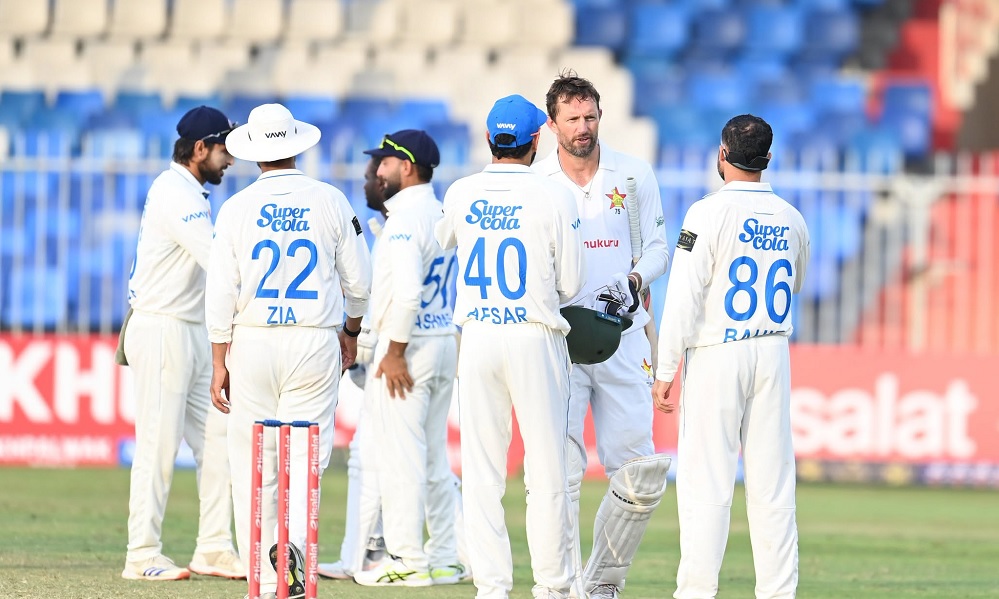
First Test between Afghanistan and Zimbabwe ends in a draw
First Muslim US senator-elect El-Sayed calls for review of aid to Pakistan
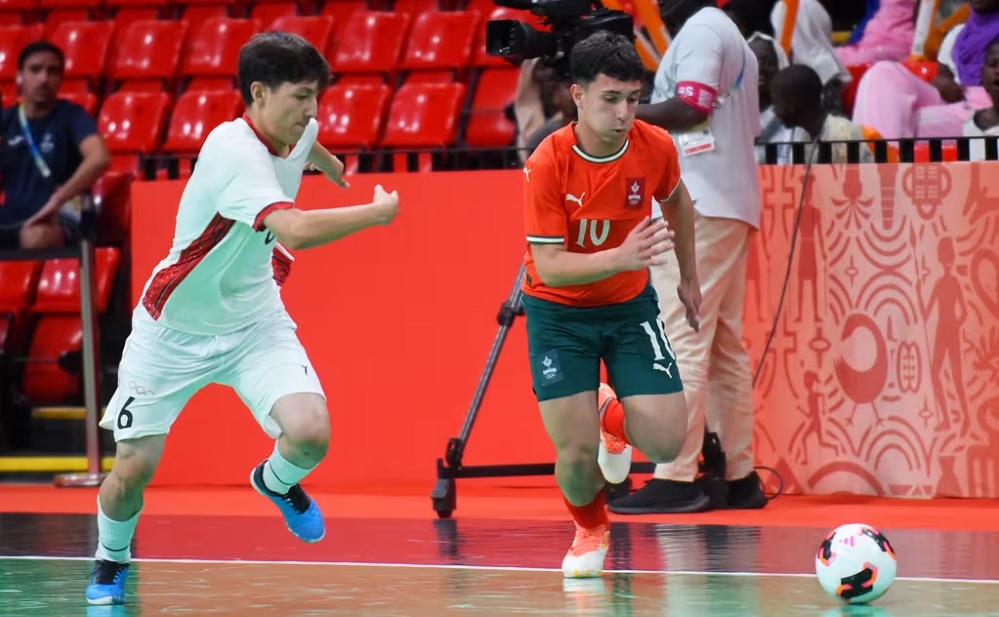
Portugal beat Afghanistan 2-0 in Dakar Youth Olympics futsal semi-finals
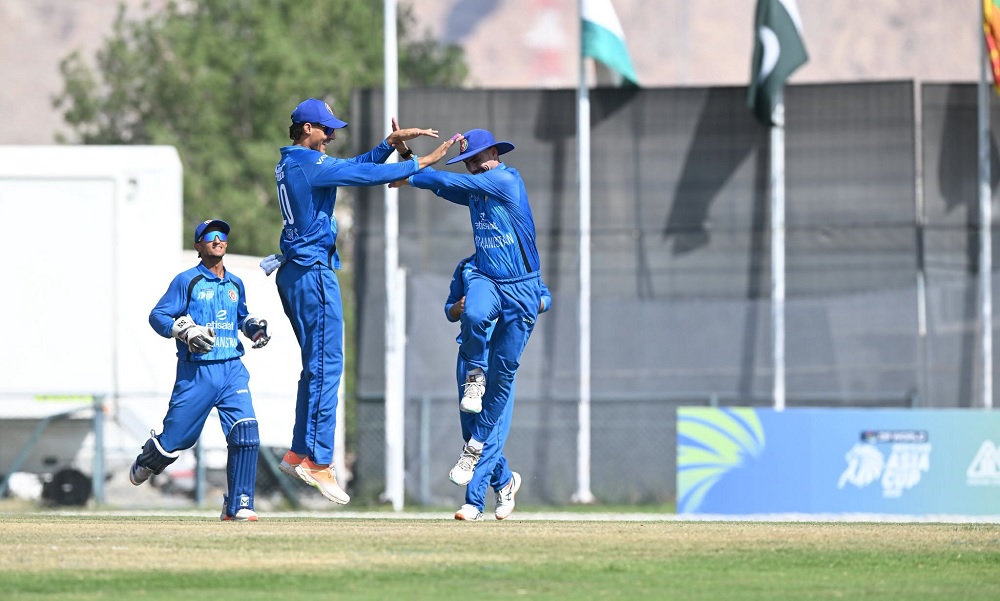
Afghanistan beat Sri Lanka by 106 runs in Under-19s Asia Cup
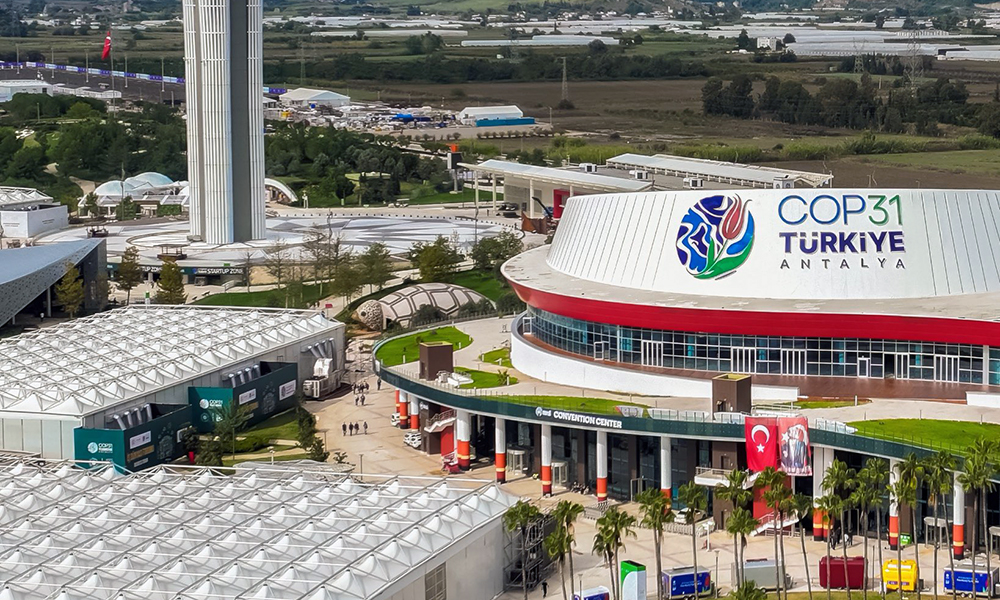
COP31 opens in Türkiye: World leaders urged to turn climate promises into action

Afghanistan finish runners-up after 6-0 defeat to Brazil in futsal final

Trump says US may strike Iran’s ‘Pickaxe Mountain’ nuclear facility

Afghan futsal coach: Brazil tournament is first step towards new goals and World Cup

Houthis warn airlines to avoid Saudi airports after deadly Riyadh attack

Pakistan deploys military to Peshawar after emergency rule declared
Tahawol: Geopolitical developments in the Middle East
Saar: EU’s engagement with Afghanistan
Tahawol: Afghanistan’s participation in Shanghai Plus security meeting discussed
Saar: Afghanistan’s declining humanitarian aid funding discussed
Tahawol: Calls for stronger joint action against terrorism discussed
-
 Sport5 days ago
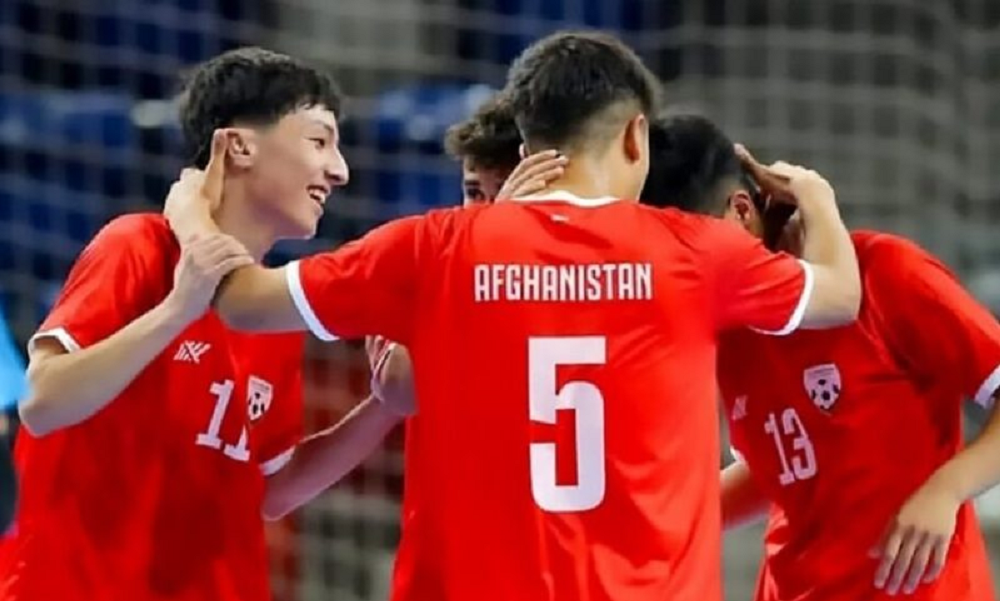
Afghanistan suffer narrow defeat against Argentina at Dakar Youth Olympics
-

 International Sports5 days ago
Cristiano Ronaldo announces international retirement
-
 Regional5 days ago
Iran says US voted ‘No to War’ after Republican midterm losses
-
 Regional5 days ago
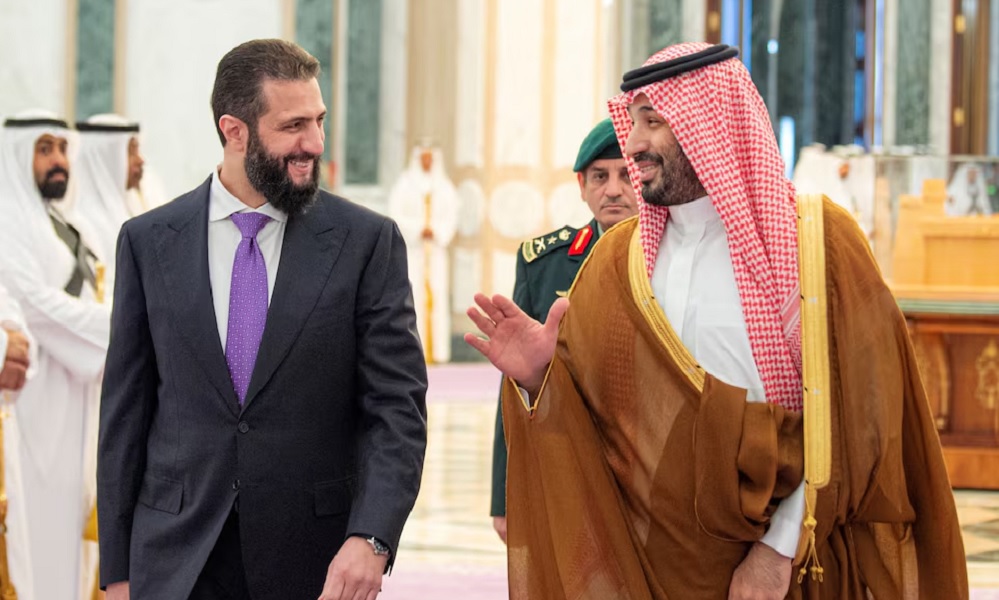
Saudi, Syrian defence ministries sign cooperation agreement
-
 World5 days ago
White House declares ‘Trump is still your president’ after Republicans suffer sweeping midterm defeats
-
 Latest News5 days ago
More than half of Afghan primary school-age children out of school: UN report
-
 Regional4 days ago
Iran sent nuclear proposal to the US via Qatar, senior Iranian official tells Reuters
-
 Sport3 days ago
Abu Muslim Farah claim convincing 3-0 win over Omar Zawak in ACL